Trusted by Engineering Teams Across Automotive, Industrial & Defense

Ashok Leyland
Tata Motors
Honeywell
Elbit Systems
Esab
CPqD
Elico
Renesas
Sierra
Ashok Leyland
Tata Motors
Honeywell
Elbit Systems
Esab
CPqD
Elico
Renesas
Sierra

Automotive Microcontroller Secure Boot, Engineered Silicon-First

Automotive microcontroller secure boot isn't a checkbox you enable in a reference manual — it's a chain of trust that has to survive production, field updates, and an attacker with a hardware debugger. Embien builds that chain from the silicon up, whether the target is NXP secure boot on an S32K or i.MX automotive part, or STM32 secure boot on an STM32 automotive-grade MCU.

Our secure boot development process starts with the hardware root of trust and HSM (Hardware Security Module) provisioning, then layers key management, signed-image verification, and rollback protection on top — the same secure bootloader implementation in embedded systems discipline whether the ECU is a body controller, a gateway, or a telematics control unit. Explore our automotive cybersecurity services for the full engineering scope behind automotive microcontroller secure boot.

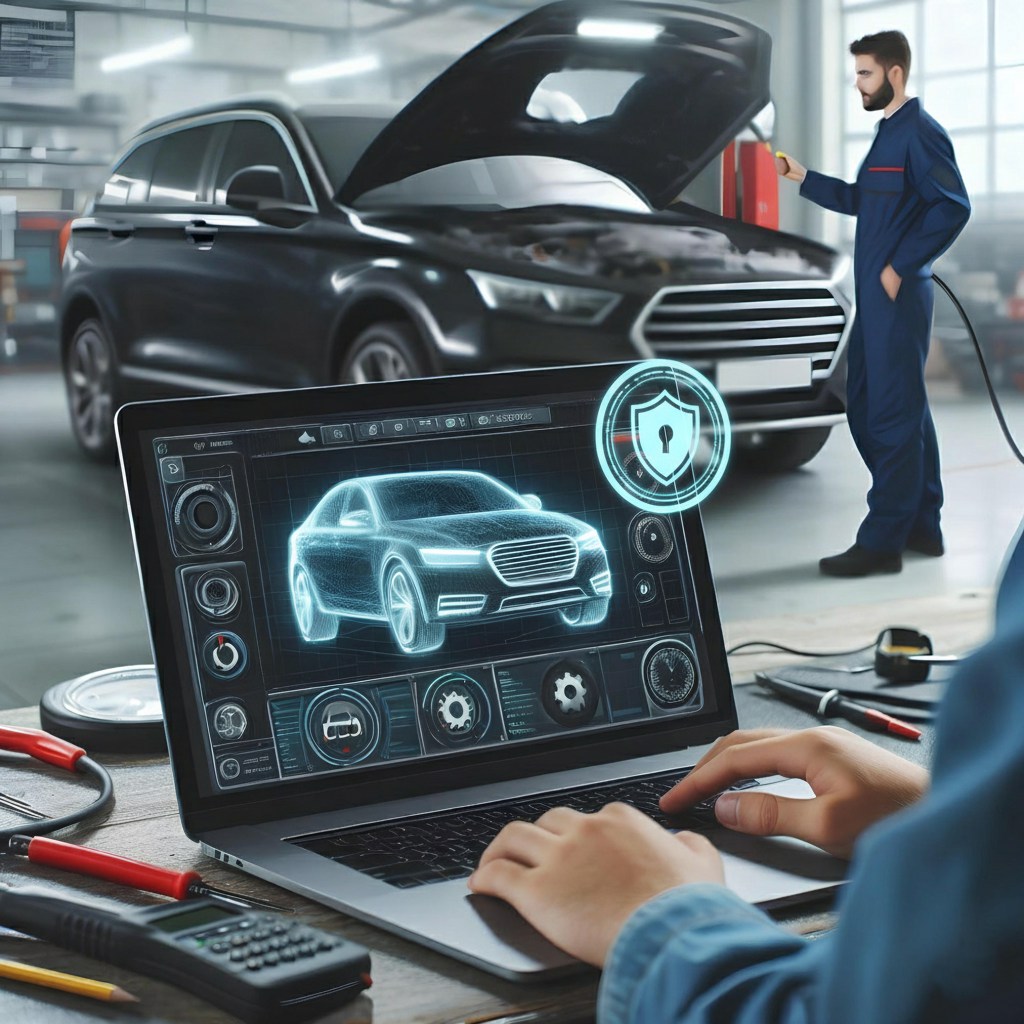
Automotive Microcontroller Secure Boot Architecture

What ECU Programs Get From Our Secure Boot & HSM Engineering

Four things automotive suppliers evaluate before choosing an automotive microcontroller secure boot partner.

Automotive Microcontroller Secure Boot

Automotive Microcontroller Secure Boot

Chain-of-trust design, signed-image verification, and rollback protection engineered for automotive microcontroller secure boot on production ECUs.

Hardware Security Module Integration

Hardware Security Module Integration

HSM provisioning and key management integrated into the secure boot development process, so cryptographic keys never live in unprotected flash.

NXP & STM32 Secure Boot Development

NXP & STM32 Secure Boot Development

Silicon-specific NXP secure boot and STM32 secure boot implementation, tuned to each vendor's HSM and secure enclave capabilities.

Secure Bootloader & Remote Updates

Secure Bootloader & Remote Updates

Secure bootloader implementation in embedded systems paired with encrypted, rollback-safe remote firmware update pipelines for fielded ECUs.

Standards Behind Our Automotive Microcontroller Secure Boot Work

ISO 21434 icon

ISO 21434

Automotive cybersecurity management applied to every secure boot development process.

Secure Boot Chain of Trust icon

Secure Boot Chain of Trust

Hardware root of trust through signed, verified boot stages for automotive microcontroller secure boot.

Hardware Security Module icon

Hardware Security Module

HSM-backed key storage and cryptographic operations for NXP secure boot and STM32 secure boot.

Automotive Penetration Testing icon

Automotive Penetration Testing

Independent validation of every secure bootloader implementation in embedded systems before production sign-off.

Production-Grade Secure Boot and HSM for Automotive TCU

Proof: Production-Grade Secure Boot, Not a Reference Design

Automotive microcontroller secure boot claims are easy to make. Here's a real one: our team enabled production-grade secure boot and HSM integration for an automotive TCU — a full secure boot development process covering hardware root of trust, HSM provisioning, and signed-image verification, taken from architecture through to a shipping ECU. It's the same secure bootloader implementation in embedded systems discipline that underpins every NXP secure boot and STM32 secure boot engagement we take on.

Questions Buyers Ask Before Choosing an Automotive Secure Boot Partner

It spans hardware root-of-trust design, HSM provisioning and key management, signed-image verification, rollback protection, and validation against fault-injection and glitching attacks — not just enabling a vendor's default secure boot fuse setting.

Ready to Discuss Your Secure Boot & HSM Program?

Tell us where your automotive microcontroller secure boot project stands. An engineer — not a sales queue — will follow up.

For further information on how your personal data is processed, please refer to the Embien Privacy Policy.