Network-layer controls like MACsec, IPsec, and TLS protect data as it moves between ECUs, but they do nothing to guarantee that the software running inside a given ECU is the software that was actually put there by the OEM or Tier 1 supplier. Secure bootloader development closes that separate gap: it verifies, cryptographically, at every power-on, that the bootloader, the application image, and any calibration data loaded onto an automotive microcontroller are authentic and unmodified before the processor is allowed to execute them. A network segment can be perfectly encrypted and authenticated and an ECU can still be compromised if nothing checks what code is actually running on it at boot; secure bootloader development is the control that closes that gap, and it has to be designed in at the silicon and boot-ROM level, not bolted on afterward.
Secure boot silicon platforms for automotive work build the trust anchor into the microcontroller itself rather than into application software, using a dedicated Hardware Security Module. The hardware security module (HSM) architecture in automotive microcontrollers typically found on platforms like Infineon AURIX, NXP S32, and Renesas RH850 pairs an isolated processing core with its own protected memory, cryptographic accelerators for AES and ECC/RSA operations, and a true random number generator, all physically separated from the main application core so that a compromise of application software cannot reach the keys or verification logic the HSM holds. Choosing among secure boot silicon platforms is one of the earliest architecture decisions an automotive program makes, because the HSM's cryptographic performance and secure storage capacity directly bound how fast a multi-image boot chain can verify and how many keys it can manage across an ECU's service life.
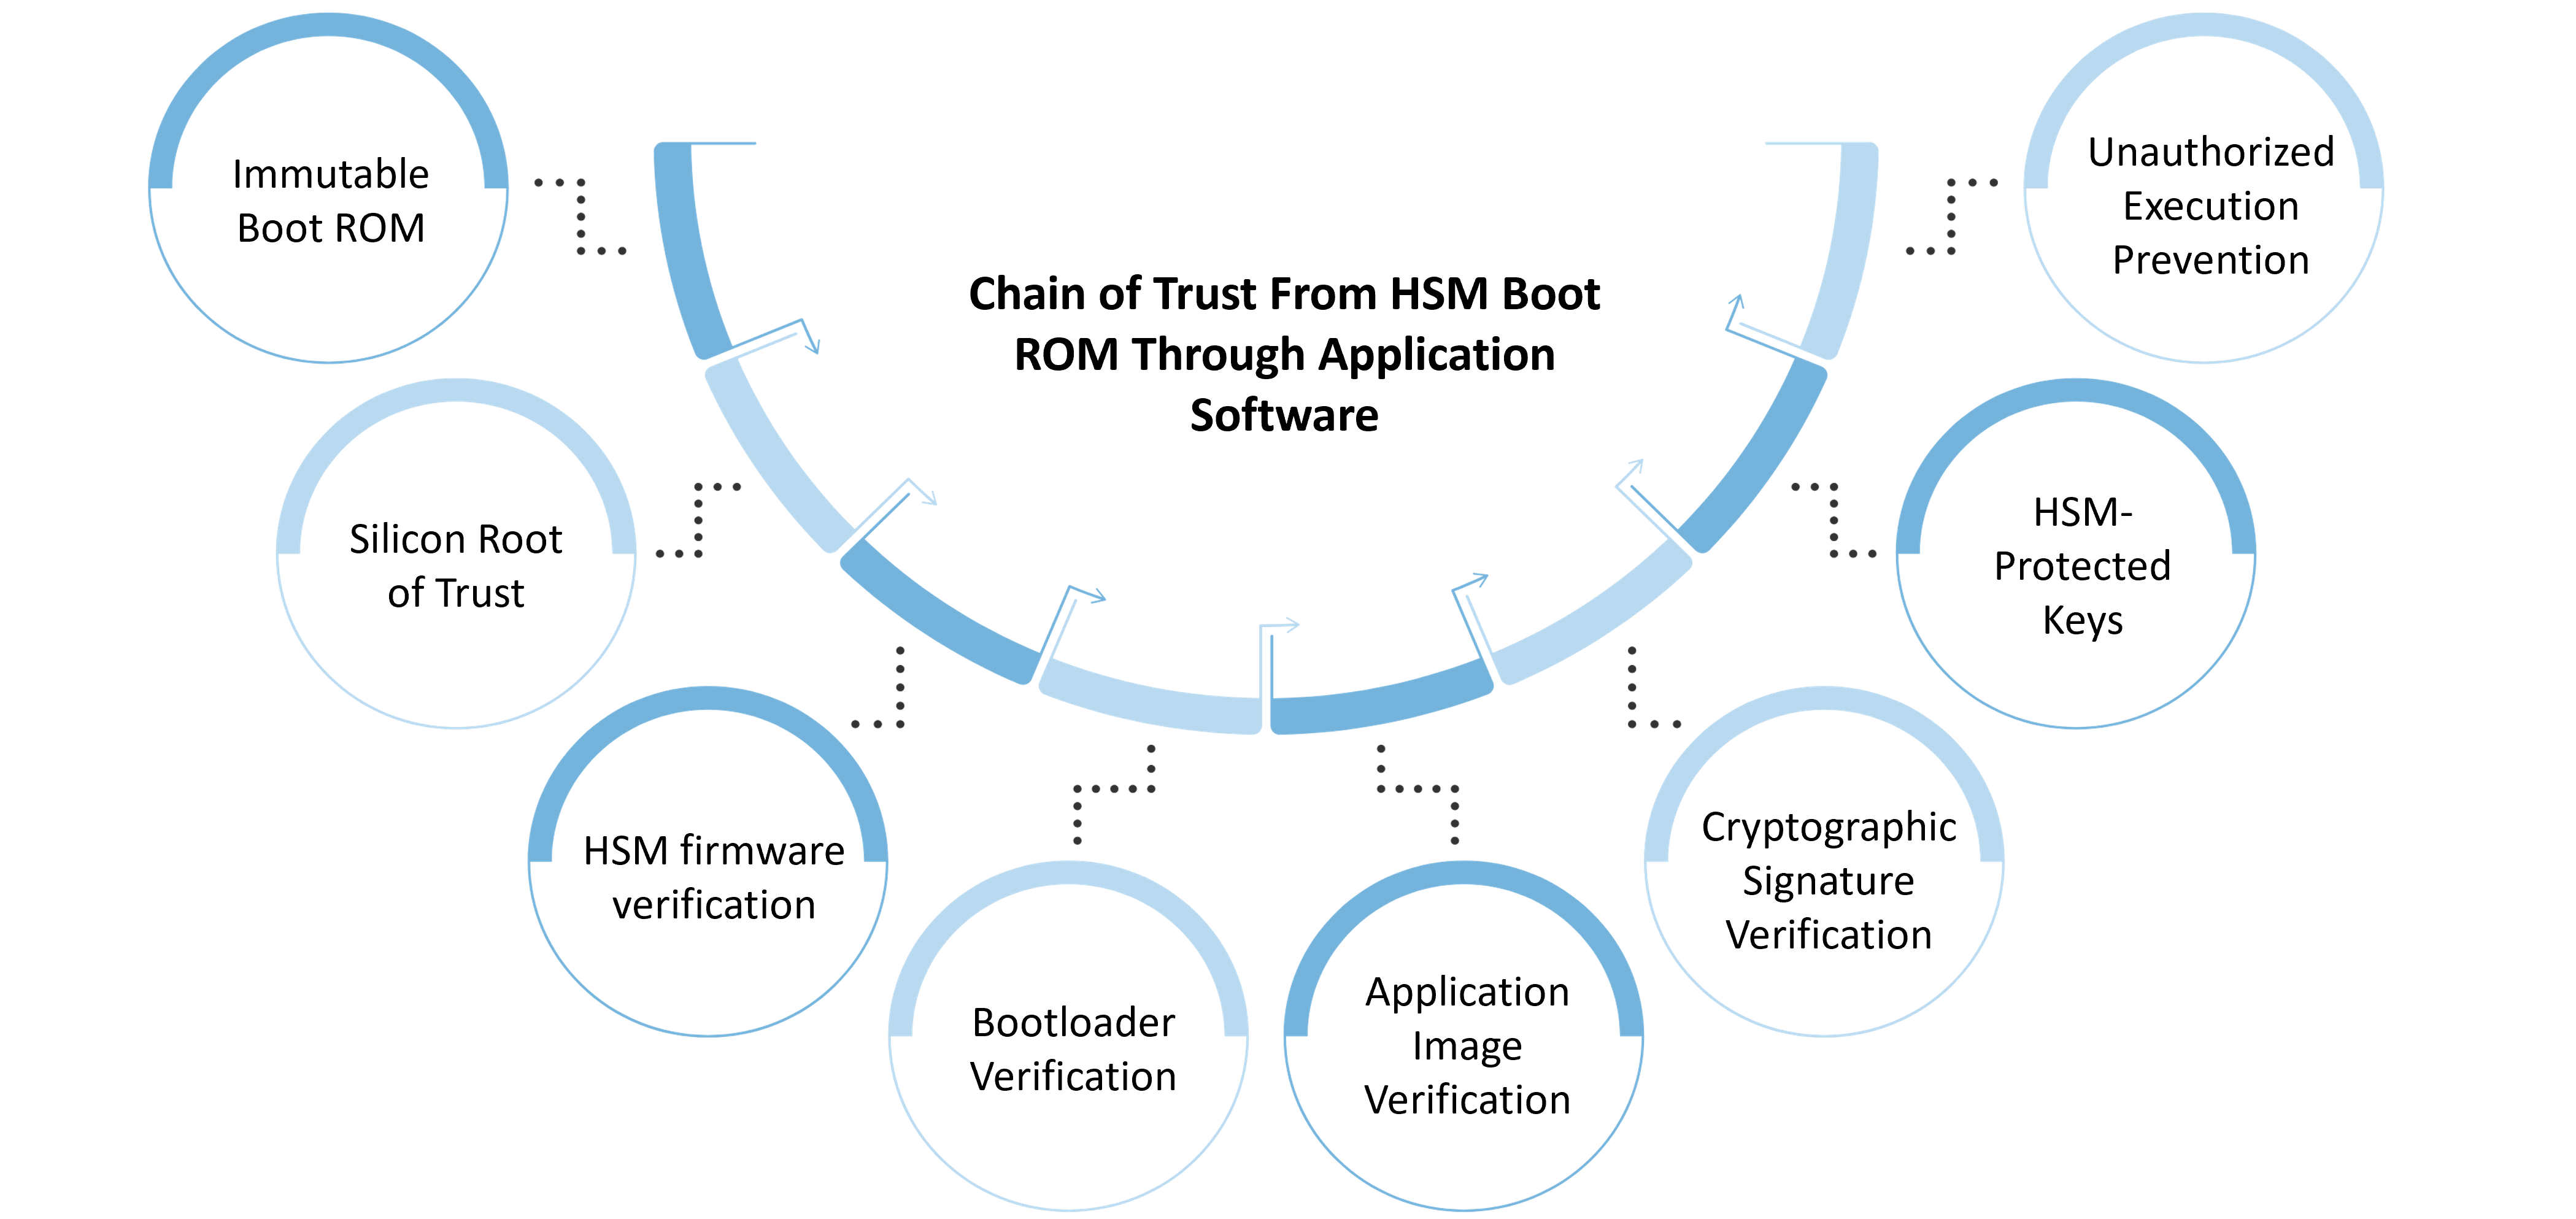
Secure boot works as a sequence of verification steps, each stage checking the integrity and authenticity of the next before handing over execution, and that sequence is what the industry calls a chain of trust from HSM boot ROM through application software. It starts at an immutable boot ROM burned into silicon at manufacturing time, a root of trust that cannot itself be modified, which verifies the signature on the HSM firmware. The HSM firmware in turn verifies the bootloader, and the bootloader verifies the application image, each link checking a cryptographic signature against a public key anchored back to that same silicon root of trust. If any single link in the chain of trust fails verification, a properly designed secure bootloader development process halts the boot rather than falling back to executing unverified code, which is the difference between a control that actually prevents unauthorized execution and one that only detects it after the fact.
Secure boot's cryptographic guarantees are only as strong as the process that gets signing keys and device-unique credentials onto the ECU in the first place. Key provisioning at manufacturing time has to inject unique keys or certificates into each unit's protected HSM storage without ever exposing the OEM's root signing key to the production line itself, typically through a hardware security module at the contract manufacturer that performs signing operations on request rather than releasing the key material. Getting key provisioning wrong, reusing one key across an entire production run, or leaving a debug-time provisioning interface enabled in production silicon, undermines everything the rest of the secure bootloader development effort was built to guarantee.
Beyond validating what runs at power-on, the same signature-verification infrastructure secure boot establishes is what a reflash procedure checks against before accepting a new image over UDS diagnostics or an OTA update channel. An ECU with a working chain of trust will refuse to flash an application image that isn't signed by a key the HSM recognizes as authorized, which is what actually prevents an attacker, or an unauthorized workshop tool, from pushing modified firmware onto a vehicle. This is also where secure bootloader development intersects directly with warranty and liability exposure: an OEM that cannot cryptographically prove what software was running on a vehicle at the time of an incident has a much harder position to defend than one that can.
Secure boot case studies are useful precisely because the theory of a chain of trust is straightforward while the production engineering, HSM firmware bring-up, key ceremony design, provisioning line integration, and boot-time performance budgeting, is where real implementations succeed or stall. Embien's own work is documented in Enabling Production-Grade Secure Boot and HSM for an Automotive TCU, covering exactly this scope for a telematics control unit: HSM-anchored chain of trust, manufacturing-time key provisioning, and reflash protection delivered as a production-ready implementation rather than a proof of concept. Reviewing secure boot case studies like this one against a program's own silicon platform and supply chain is a faster way to scope the engineering effort than starting from the standard's text alone.
Secure bootloader development is not an isolated feature; it is one of the cybersecurity controls a TARA under ISO 21434 is likely to identify as necessary once unauthorized reflashing or firmware tampering is scored as a credible threat scenario. Programs building out a broader cybersecurity engineering lifecycle, covered in our ISO 21434 explainer, should expect secure boot to appear as a required control on any ECU where the TARA scores firmware tampering as a meaningful risk, with the CAL assigned to that goal shaping how rigorously the chain of trust needs to be verified and tested.
Embien Technologies designs and implements secure bootloader development across automotive microcontroller platforms: HSM architecture bring-up, chain-of-trust design from boot ROM through application software, manufacturing-time key provisioning, and reflash protection, informed by production experience including the TCU work covered in our secure boot case studies. General embedded secure boot background for teams outside the automotive domain is available on our secure boot for embedded systems page. To scope a secure bootloader development effort for an upcoming ECU program, reach out to Embien's engineering team.

Edge Computing Services support secure and efficient embedded computing through optimized hardware platforms, real-time processing, and reliable software integration for automotive and industrial applications.
Explore secure boot implementation for embedded systems, including cryptographic image verification, chain-of-trust design, firmware integrity, and protection against unauthorized code execution.
A case study on implementing production-grade secure boot and Hardware Security Module integration for an automotive TCU, covering chain-of-trust design, key provisioning, and firmware reflash protection.