
Introduction
Most vehicle cybersecurity content, including plenty on this site, covers ISO 21434 compliance and threat modeling done before a vehicle ships. Far less gets written about what actually happens after something goes wrong: how a real automotive cyber incident gets detected, who's actually responsible for responding, and how the decision between an OTA fix and a physical recall gets made under real time pressure. What happens when a car gets hacked: automotive incident response is a distinct discipline from prevention, and one every ISO 21434-compliant program still needs a real answer for, because compliance reduces the likelihood of an incident, it doesn't eliminate the need to respond well when one occurs anyway.
In short: automotive cybersecurity incident response and remediation has to be planned as its own workstream, with defined roles across OEM, Tier 1 suppliers, and connectivity providers, before an incident happens, because figuring out who owns what during a live incident is far more expensive and far slower than having answered it in advance.
What a Real Automotive Cybersecurity Incident Looks Like in Practice
Automotive cybersecurity incidents rarely look like the cinematic scenario of a single hacker seizing full vehicle control mid-drive. Real incidents more commonly involve a vulnerability discovered in a connected service, a telematics API, an infotainment update mechanism, a key fob relay attack, that could be exploited at scale across a vehicle fleet, discovered either through responsible disclosure by a security researcher, internal security testing, or in less fortunate cases, active exploitation observed in the field. The scale question matters enormously: a vulnerability affecting one vehicle is a service issue, the same vulnerability affecting a shared platform across hundreds of thousands of vehicles is a fleet-wide incident with correspondingly different response obligations.
Detection: How OEMs and Suppliers Typically Learn About a Breach
Detection paths vary widely in how much warning they give a response team. Responsible security researcher disclosure, increasingly common as automotive bug-bounty programs mature, typically gives an OEM weeks of lead time before public disclosure. Internal security monitoring, anomaly detection on telematics or OTA infrastructure, can catch active exploitation in progress, giving less lead time but earlier awareness of real-world impact. The least favorable path, public disclosure or active exploitation discovered through customer reports or media coverage, gives essentially no lead time and forces incident response and public communication to happen simultaneously, which is precisely why building strong relationships with the security researcher community and investing in proactive fleet monitoring both reduce how often an OEM ends up in that worst-case detection scenario.
Incident Response Roles Across OEM, Tier 1, and Connectivity Providers
A modern connected vehicle's cybersecurity incident rarely implicates a single party cleanly. The OEM typically owns overall vehicle safety and regulatory disclosure obligations regardless of where in the supply chain a vulnerability originated. The Tier 1 supplier that developed the affected ECU or software component typically owns the technical root-cause analysis and fix development for that component. And a connectivity or cloud service provider, if the vulnerability involves telematics, OTA infrastructure, or a connected app, often owns a distinct piece of the technical response entirely outside the vehicle itself. Without a pre-agreed incident response plan defining exactly who is responsible for what within this chain, during a live incident, precious time gets lost simply establishing whose problem a given vulnerability actually is before anyone starts fixing it.
Vehicle Hacking Threat Categories and Why Response Plans Need to Cover Each Differently
Different vehicle hacking threat categories demand meaningfully different response approaches. A vulnerability in an infotainment system, while serious for privacy and potentially for lateral movement to safety-critical networks, is typically remediable through a conventional OTA software update. A vulnerability affecting a safety-critical ECU directly, brake, steering, or powertrain control, carries a fundamentally different risk profile and may require immediate mitigating action, a functional restriction pushed remotely, alongside the longer-term fix. And a vulnerability in shared cloud or connectivity infrastructure affecting multiple vehicle lines or even multiple OEMs sharing a supplier's platform can require coordinated response across organizations that don't otherwise share incident response processes. A single generic incident response plan that doesn't distinguish between these categories will handle none of them well.
Threat Modeling for Automotive Cybersecurity: Where Prevention Meets Response Planning
Threat modeling for automotive cybersecurity, the TARA (Threat Analysis and Risk Assessment) process ISO 21434 requires, isn't just a pre-launch compliance exercise, its outputs should directly inform incident response planning. A TARA that identified a specific attack path as high-risk but accepted it with a specific monitoring or mitigation control in place gives an incident response team a head start if that exact path is ever actually exploited: the analysis of impact and likely attack progression already exists, rather than needing to be developed from scratch under incident-response time pressure. Programs that treat TARA as a one-time compliance deliverable, filed away after approval, are leaving this response-planning value on the table.
Remediation via OTA vs. Recall: How That Decision Gets Made
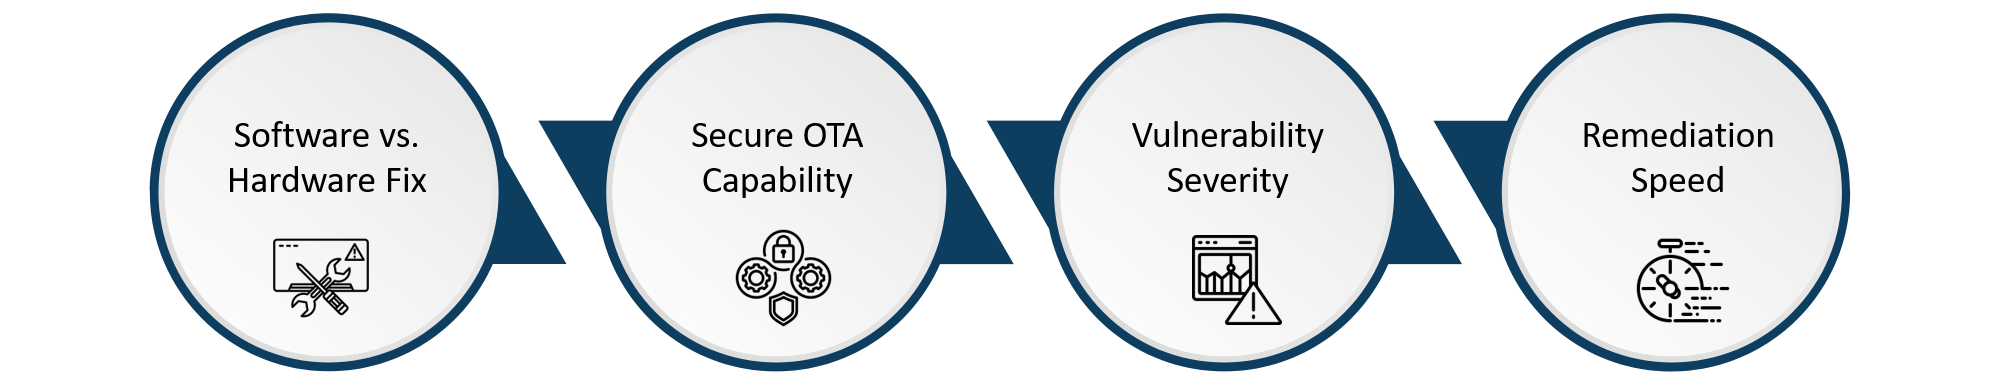
The decision between an over-the-air software remediation and a physical recall hinges on a few key factors: whether the vulnerability can be fully addressed through a software change alone or requires a hardware modification, whether the affected ECU has secure OTA update capability already deployed and validated in the field, and the severity and exploitability of the vulnerability weighed against the practical reality that an OTA update reaches a fleet in days while a recall can take months to complete. This is precisely why building secure, validated OTA update infrastructure into a vehicle program from the start, not as an afterthought, materially changes an OEM's remediation options and response speed when the next serious cybersecurity finding surfaces.
Regulatory Disclosure Obligations After an Automotive Cyber Incident
UNECE WP.29 R155's Cybersecurity Management System requirements, now mandatory for new vehicle type approvals in UNECE member markets, extend beyond pre-launch compliance into ongoing monitoring and incident response obligations, including reporting cybersecurity incidents through the OEM's Cybersecurity Management System processes. Depending on jurisdiction and incident severity, additional regulatory or contractual disclosure obligations, to type-approval authorities, to affected customers, or to Tier 1 partners whose components were implicated, may also apply. An incident response plan that doesn't have these disclosure obligations mapped out in advance risks missing a regulatory deadline simply because no one identified which obligation applied until well into the response.
What This Means for How ECUs Should Be Designed for Recoverability
The single design decision that most improves an OEM's incident response options is building secure OTA update capability, with cryptographically verified, rollback-capable firmware updates, into safety-relevant ECUs from the program's start, not retrofitted after a vulnerability is found. An ECU designed for recoverability, capable of receiving a validated remote update, capable of falling back to a known-good state if an update fails, and instrumented to confirm a remediation was successfully applied across the fleet, gives an OEM options during an incident that an ECU without that capability simply doesn't have, often the difference between a fast, low-cost OTA remediation and a slow, expensive recall.
Embien's Capabilities
Embien brings automotive cybersecurity engineering experience spanning ISO 21434 TARA processes, secure OTA update infrastructure, and secure development lifecycle practices aligned with ISO 21434 and IEC 62443. Our engineering process treats OTA remediation capability as a core design requirement for safety-relevant ECUs, not an afterthought, giving programs real recoverability options if a cybersecurity incident ever needs a fast, field-wide response.
To discuss cybersecurity architecture, TARA, or secure OTA update infrastructure for a connected vehicle program, reach out to Embien's engineering team.